Apply packet filtering in Wireshark for cellular traffic, verify firewall rules at signaling boundaries, and audit protocol parameter bounds.
📖 Briefing Coverage Scope
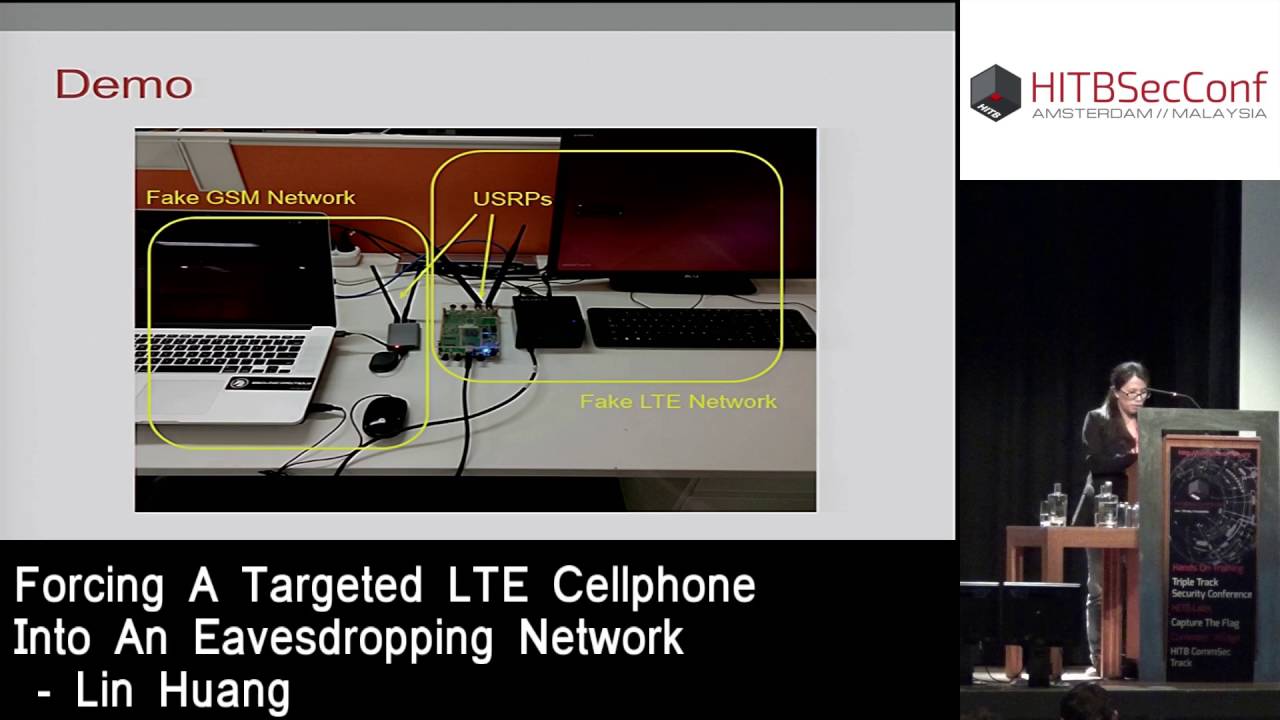
In this presentation, we will introduce a method which jointly exploits the vulnerabilities in tracking area update procedure, attach procedure, and RRC redirection procedure in LTE networks resulting in the ability to force a targeted LTE cellphone to downgrade into a malicious GSM network where an attacker can subsequently eavesdrop its voice calls and GPRS data.
STUDY BRIEFING DOSSIER EXPORTER EXPORT COMPLETE LAB NOTES & TIMESTAMPS FOR NOTION / OBSIDIAN
5G SBA NRF Service Discovery & OAuth2 Token Abuse
5G-SBA
Call flow illustrating how an unauthenticated Network Function (Rogue NF Consumer) queries the NRF for discovery and retrieves access tokens without adequate TLS mutual auth or token scoping.
Entity 01Rogue NF Consumer (AMF)
Entity 02NRF (Discovery & Auth)
Entity 03Target NF Producer (UDM)
1
1. GET /nnrf-disc/v1/nf-instances?target-nf-type=UDMREQUEST
Rogue NF Consumer (AMF) ➔ NRF (Discovery & Auth)
2
2. 200 OK (UDM Endpoint URI & Supported Services)RESPONSE
NRF (Discovery & Auth) ➔ Rogue NF Consumer (AMF)
3
3. POST /oauth2/token (grant_type=client_credentials, scope=nudm-sdm)EXPLOIT
Rogue NF Consumer (AMF) ➔ NRF (Discovery & Auth)
4
4. 200 OK (Access Token: Bearer eyJhbGciOi...)RESPONSE
NRF (Discovery & Auth) ➔ Rogue NF Consumer (AMF)
5
5. GET /nudm-sdm/v1/imsi-208950000000001/am-dataEXPLOIT
Rogue NF queries NRF discovery endpoint to enumerate registered UDM instances in PLMN.
Technical Term & Subtitle Translator
Inspect Technical Acronym:
5G-SBA — 5G Service Based Architecture
5G Core
🇺🇸 English
Core network architecture in 5G Standalone (SA) where Network Functions (AMF, SMF, NRF, UDM) communicate via HTTP/2 REST APIs with OAuth2 authentication.
⚠️ Security Vectors & Exploitation Note:
Vulnerable to NRF token abuse, unauthorized REST discovery, and API gateway parameter tampering.
About this signal
In this presentation, we will introduce a method which jointly exploits the vulnerabilities in tracking area update procedure, attach procedure, and RRC redirection procedure in LTE networks resulting in the ability to force a targeted LTE cellphone to downgrade into a malicious GSM network where an attacker can subsequently eavesdrop its voice calls and GPRS data.
SIGINT DISPATCH // BRIEFING DISCLOSURES
Intercepted Telecom Security Intelligence
Weekly briefings on 3GPP signaling CVEs, baseband reverse engineering, 5G SBA vulnerabilities, and packet captures.